Bitcoin insights and practical guides
By Crypto Dispensers · Updated October 15, 2026
Bitcoin wallet security
That can reduce dependence on one key, but it also introduces more things to maintain. Recovery depends on the signing threshold, your usable backups and the information needed to reconstruct the wallet. More devices do not automatically mean better protection.
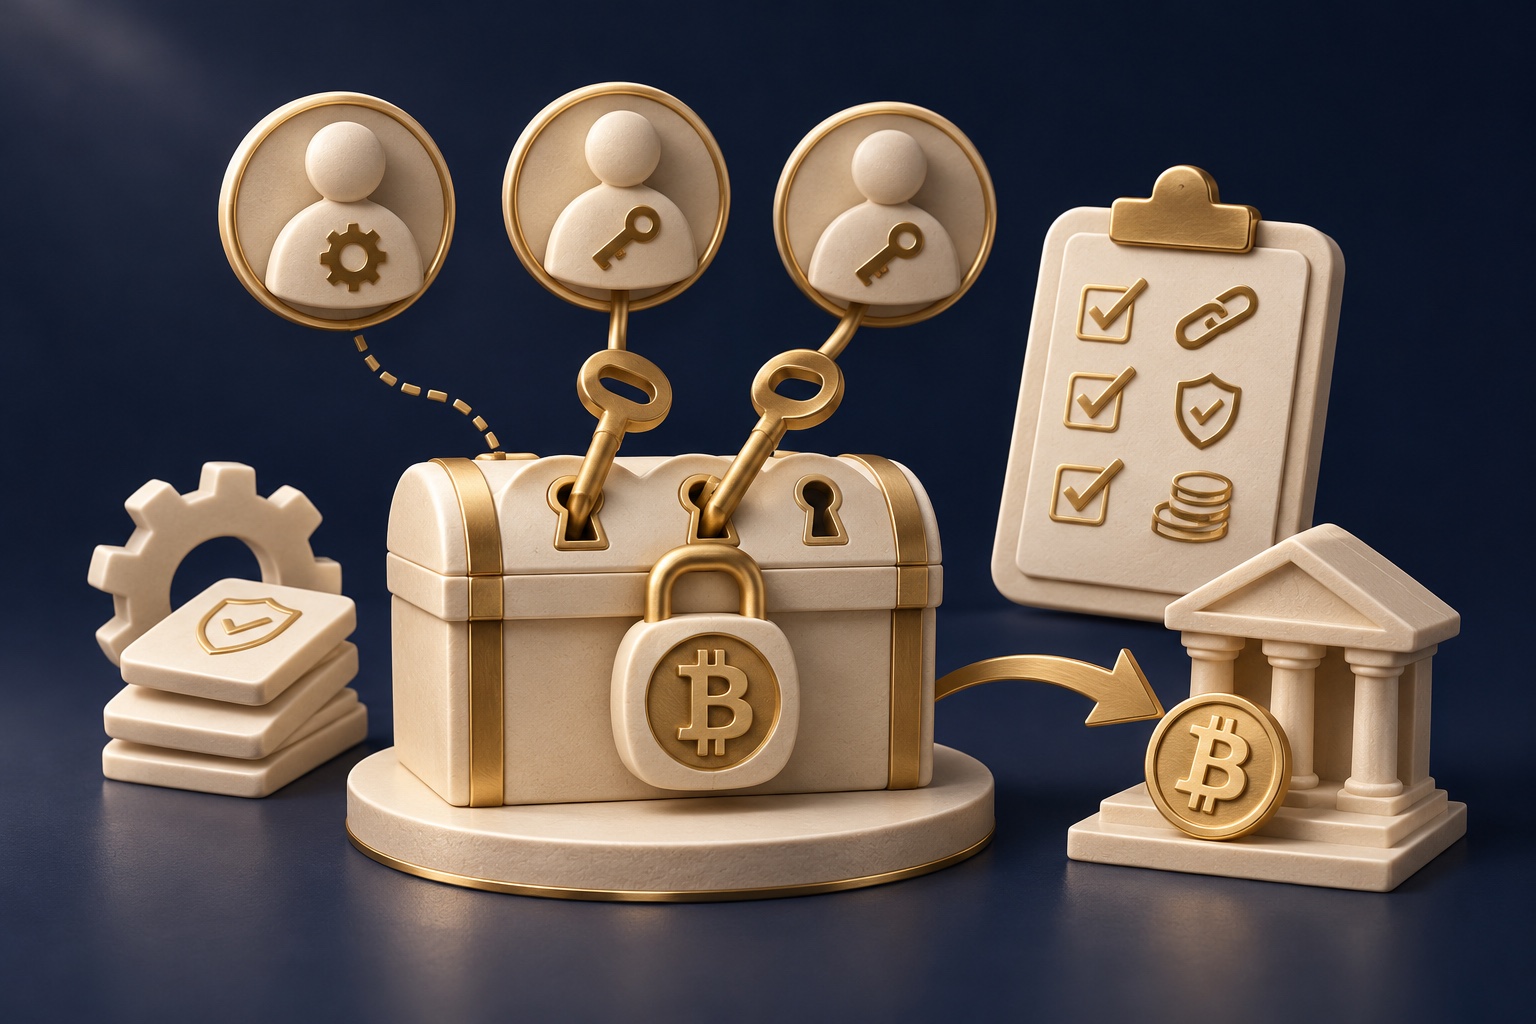
The first number is the number of signatures required. The second is the number of participating keys. A conventional 2-of-3 policy allows the pairs A+B, A+C or B+C to sign. It does not require a particular pair or all three keys.
For comparison, a 2-of-2 wallet needs both designated keys. Electrum's multisig documentation illustrates a two-cosigner workflow: one signs a transaction, the other adds the required signature, and the completed transaction can then be broadcast.
The following scenarios are illustrations of the threshold rule. Assume three independently generated signers, the complete wallet configuration is available, and there is no alternative recovery condition. “Unavailable” means neither the key nor a usable backup can be accessed; “compromised” means an attacker can sign with it.
| Situation | Result under a 2-of-3 rule |
|---|---|
| Key A is unavailable; B and C remain accessible | B and C can still authorize a spend |
| An attacker controls A only | A alone cannot authorize a spend |
| A and B are unavailable; only C remains | C cannot meet the signing threshold |
| An attacker controls A and B | The attacker can meet the threshold without C |
If a device is stolen, the risk depends on its protections and what the attacker can access. Exposed recovery words may let someone recreate a key on another device. Check how many signing keys are still usable and secure.
A signer controls a private key and uses it to approve a transaction. A coordinator helps assemble the wallet configuration and manage the signing workflow. These roles may be implemented by separate applications and devices.
BIP 129, Bitcoin Secure Multisig Setup, describes how a coordinator gathers public-key information and returns a wallet descriptor to signers. Each signer checks its participation. This is a setup specification, not a guarantee that every wallet supports the same workflow.
Public information used to construct addresses is different from the secret material used to sign. You do not need to give every participant every recovery phrase to establish a multisig wallet. Doing so can defeat the separation you intended.
The coordinator's role also does not make it harmless. Incorrect or tampered setup information can produce the wrong receiving addresses. BIP 129 specifically addresses configuration integrity and privacy concerns. Follow the chosen wallet's process for verifying the policy and addresses on trusted signing devices, rather than relying only on a computer display.
If those terms are unfamiliar, first review private keys and Bitcoin wallets.
Select the independently usable keys in a hypothetical 2-of-3 wallet. Assume the correct wallet configuration is available and there is no separate recovery condition. This demonstration does not connect to a wallet or authorize a transaction.
The permitted pairs are A+B, A+C and B+C. One usable key cannot meet this rule. An attacker with two usable keys may be able to spend. The boxes count keys, not devices, people or copies of a seed.
Receiving Bitcoin and later spending it are separate operations. A sender pays to a Bitcoin address; your wallet’s spending policy controls the later spend. A successful receive does not prove you can recover or operate the wallet.
Your selections are only a preparation aid. Follow the instructions for your current request.
Our wire service delivers Bitcoin to a confirmed wallet after the required review and final-price approval. Contact our team before funding if you plan to use multisig. This article does not establish support for every multisig configuration, a shared-custody service or a test-purchase option.
Keep recovery words and private keys private. A wallet configuration can also reveal private financial activity even when it cannot sign. BIP 129 explains checking the setup across signers; Unchained’s configuration guide explains why recovery can require more than seed backups.
Plan for two different needs: recovering enough signing keys and reconstructing the correct wallet. A collection of recovery phrases should not be treated as a complete, tested multisig recovery plan.
The wallet configuration records how the keys fit together. Depending on the format, this includes the threshold, public keys or extended public keys, derivation paths and script type. Unchained's wallet-configuration explanation describes why multisig recovery needs these details. A 2-of-3 wallet still includes three participants' public-key information even though only two signatures are needed to spend.
Keep the export or descriptor your wallet documents for recovery, along with clear instructions identifying the intended setup. Protect its privacy: public-key configuration can expose wallet activity even when it cannot sign transactions by itself. Check exactly what an export contains; a general wallet backup may contain more sensitive material than a public descriptor.
COLDCARD's multisig documentation lists the policy and cosigner information its setup requires and recommends testing recovery before depositing funds. Follow the current guidance for the specific software and devices you use, including relevant firmware notices.
Separate locations can reduce the chance that one incident affects all signers and backups. But separation only helps if you can still retrieve the required materials when needed. A plan that depends on an inaccessible device, forgotten passphrase or missing configuration can leave funds unavailable.
No. The spending rule and the people controlling its keys are separate questions. One person can manage all signers. Several people can share them. A service can participate as a cosigner. To understand control, ask who can assemble enough signatures without anyone else's cooperation.
As an illustrative 2-of-3 arrangement, suppose you control A and B and a service controls C. A+B can satisfy the threshold without C. If you control only A while the service controls B and C, that service can satisfy it without you. Those examples assume the simple policy described above; actual services may include additional conditions, procedures or dependencies. Read the arrangement rather than inferring control from the word “multisig.” See custodial versus noncustodial wallets for the broader distinction.
Making three copies of the same recovery phrase does not create three independent signers. Each copy restores the same underlying key material. It may provide backup redundancy, but it does not create a 2-of-3 spending rule. Cutting one phrase into pieces is also a different operation from constructing a multisig wallet.
Multisig adds coordination, compatibility and recovery work. It can make routine spending slower because multiple signers must participate. Whether that tradeoff suits you depends on the problem you are trying to solve and whether you can maintain the setup.
Use this checklist to evaluate a setup before relying on it:
Keep this as a preparation guide, not a substitute for your wallet's current setup instructions. For related fundamentals, read what a seed phrase is and why hardware wallets are used. Choose a custody process you can verify, recover and continue to maintain.
Not sure how to pay? Compare wire, ACH, debit card, and credit card purchases. Each has different costs and timing. Ask our team if you need help choosing.
Compare Bitcoin buying options →Published by Crypto Dispensers, which offers crypto buying, selling and swapping services. This article is educational. Bitcoin prices can fall; fees, timing, eligibility and available services vary. Review the applicable terms before you transact.
Optional guide · Wallets and recovery
This is optional reading related to stage 4. Return to the course for its lesson, example and check.
Your Crypto Dispensers account
Create an account to see the services available to you. You can buy Bitcoin by wire, debit, credit or ACH, sell supported crypto for a USD bank payout, or exchange supported assets. Contact our team if you need help choosing a service.
Creating an account does not authorize a payment. Availability depends on your location, account and required checks.
Helping people access Bitcoin since 2017.
Privacy controls
Necessary cookies are always on so the site works. You can also allow analytics to help us improve the experience, and advertising cookies to measure campaigns and show more relevant ads. You can change this anytime.
Read our privacy policy